Embed Security Across Your Development Lifecycle
Tantrija strengthens your software delivery with secure DevOps consulting services, integrating security at every stage of your pipeline — from code to deployment. Our DevOps consultants help you build secure, compliant, and scalable infrastructure using Terraform, Kubernetes, AWS, GitHub Actions, and other modern tools. As a trusted DevOps consulting company, we ensure your DevOps practices are both fast and secure, supporting a DevOps-first culture.
Our DevSecOps Services
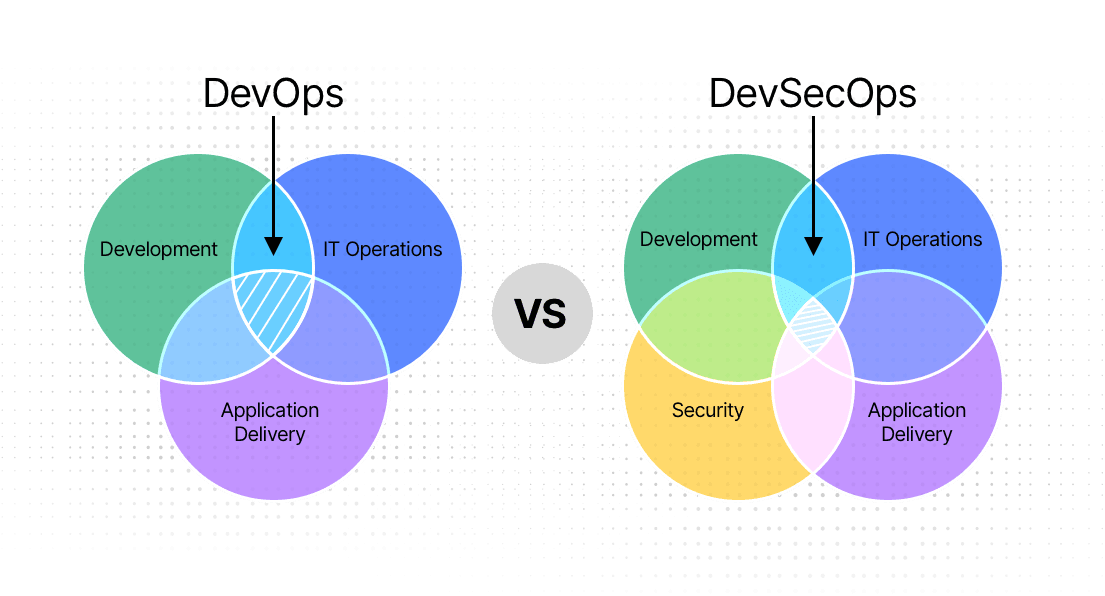
At Tantrija, DevSecOps consulting goes beyond tools — it’s about building a secure culture, automation, and continuous compliance. Our DevOps consultants help teams shift left, reduce vulnerabilities early, and maintain cloud-native agility without compromise, offering comprehensive DevOps consulting services for security-first delivery.
CI/CD Pipeline Hardening
We secure your continuous integration and delivery workflows across Jenkins, GitHub Actions, GitLab CI/CD, or Bitbucket. Our DevOps consulting firm implements secrets management, code signing, vulnerability scanning, and artifact validation to safeguard your pipelines.
Cloud Infrastructure Security
As a trusted DevOps consulting company, we secure AWS, Azure, and GCP environments with identity management, policy-as-code, threat detection, CIS benchmarks, IAM controls, and cloud-native tooling like AWS GuardDuty and Security Hub.
Infrastructure as Code (IaC) Security
Our DevOps consultants scan and secure Terraform, CloudFormation, or Pulumi templates. We enforce best practices, detect misconfigurations, and prevent security drift at the code level before deployment.
Container & Kubernetes Security
Harden your Docker and Kubernetes workloads with image scanning, pod security policies, RBAC hardening, runtime monitoring, and compliance integration using tools like Falco and Kyverno — a core offering of our DevOps consulting services.
Static & Dynamic Code Analysis (SAST/DAST)
Automate static and dynamic testing in your CI/CD pipelines. Our DevOps consulting firm integrates SonarQube, Semgrep, ZAP, and other scanners into your workflows with alerting and remediation.
Compliance Automation (SOC2, ISO, HIPAA)
Streamline regulatory compliance with automated evidence collection, policy enforcement, and continuous monitoring. Our DevOps consulting company helps you build pipelines that meet SOC 2, ISO 27001, GDPR, HIPAA, and other standards.
Security as Code & Policy Enforcement
Turn security into reusable, auditable code using OPA, Sentinel, or Rego. Our DevOps consultants enforce security gates in every deployment, making compliance continuous and scalable.
DevSecOps Maturity Assessment & Roadmap
Evaluate your current security posture and get a tailored roadmap. Our DevOps consulting services assess people, process, and tools, providing actionable steps to mature your DevSecOps capabilities.
Architecture Overview
The real technology layers behind a DevSecOps Solutions engagement.
Cloud Platform
AWS
Compute, storage, and managed services.
Containerization
Docker
Consistent, portable deployments across environments.
CI/CD
GitLab
Automated build, test, and deployment pipelines.

Services
Node.js
Application services running on the platform.
Benefits
Security by Design
Shift Left with Confidence
Our DevOps consultants embed security at every phase of development — from planning to deployment. With expert DevOps consulting services, we help you minimize risks, reduce late-stage fixes, and build secure pipelines from the ground up.
Explore More Services In This Category
Every other real, in-production service we offer alongside this one.
/ Why Choose Us
Why Choose Tantrija for DevSecOps Consulting?
We embed security into every stage of your software delivery—combining DevOps automation with rigorous security practices, hands-on enablement, and compliance-by-design.
Expert DevOps Consultants
Our experienced consultants bring deep, hands-on expertise in CI/CD, cloud infrastructure, containerization, and security automation to harden your delivery pipelines.
Comprehensive DevSecOps Consulting Services
End-to-end offerings from pipeline design and IaC security to SAST/DAST integration, secrets management, compliance automation, and DevSecOps maturity assessments.
Trusted DevOps Consulting Company
We implement scalable, secure, and automated delivery pipelines that accelerate time-to-market, reduce risk, and align with industry standards and regulations.
Tailored Solutions for Your Team
Beyond implementation, we train and enable your teams with documentation and knowledge transfer—fostering a DevOps-first culture that can scale independently.
Proven Track Record
From startups to enterprises, we’ve helped clients increase delivery speed, reliability, and security—ensuring long-term success without vendor lock-in.
/ Our Process
Our DevSecOps Consulting Process
At Tantrija, our structured DevSecOps consulting approach embeds security throughout the software delivery lifecycle. Our consultants follow a repeatable process to help organizations build secure, automated, and compliant pipelines.
Security Assessment & Strategy
We evaluate your current DevOps workflows, cloud infrastructure, and security posture, then create a roadmap to embed security from code through deployment.
Pipeline & Infrastructure Hardening
We implement CI/CD pipeline security controls, harden containers and Kubernetes, apply Infrastructure-as-Code safeguards, and add automated compliance checks.
Implementation & Automation
We integrate SAST/DAST, secrets management, policy-as-code, and end-to-end monitoring across pipelines—ensuring automation drives both speed and security.
Training & Enablement
We provide hands-on training so your teams can adopt a DevOps-first culture with a security-first mindset and confidently operate the toolchain.
Continuous Improvement & Compliance
We establish continuous security monitoring, policy updates, and compliance automation to keep DevSecOps practices effective, auditable, and scalable.
/ FAQs
Frequently Asked Questions
What is DevSecOps and why is it important?
DevSecOps integrates security into every stage of the DevOps lifecycle. We implement automated security controls, compliance checks, and monitoring to reduce vulnerabilities and deliver secure software faster.
What DevSecOps consulting services do you offer?
We provide end-to-end services including CI/CD pipeline security, Infrastructure as Code (IaC) hardening, container and Kubernetes security, compliance automation, and DevSecOps maturity assessments.
How can a DevOps consulting company help my organization?
A trusted partner like Tantrija designs, implements, and maintains secure, automated, and scalable pipelines while enabling your teams to adopt a DevOps-first culture for long-term capability.
Who are your DevOps consultants?
Our experienced consultants specialize in CI/CD, cloud infrastructure, containerization, and DevSecOps. They work closely with your team to implement best practices and provide hands-on training.
How do you ensure compliance in DevSecOps pipelines?
We integrate compliance automation for SOC2, ISO 27001, HIPAA, GDPR, and other standards—using policy-as-code, automated evidence collection, and continuous monitoring to keep pipelines audit-ready.
What makes Tantrija different from other DevOps consulting firms?
We combine implementation, automation, and team enablement. Our consultants focus on building secure, scalable, and automated pipelines while fostering a DevOps-first culture across your organization.
Security is not a patch — it's a strategy.